
Suppliers, contractors, and engineers use your web apps across every plant — yet your controls stop at login.





Which access workflow is worth tightening first?
Start with the enterprise web apps your suppliers, contractors, and engineering teams use every day. Look at who needs access, the devices involved, and how your business and engineering data should move.
Supplier and contractor access
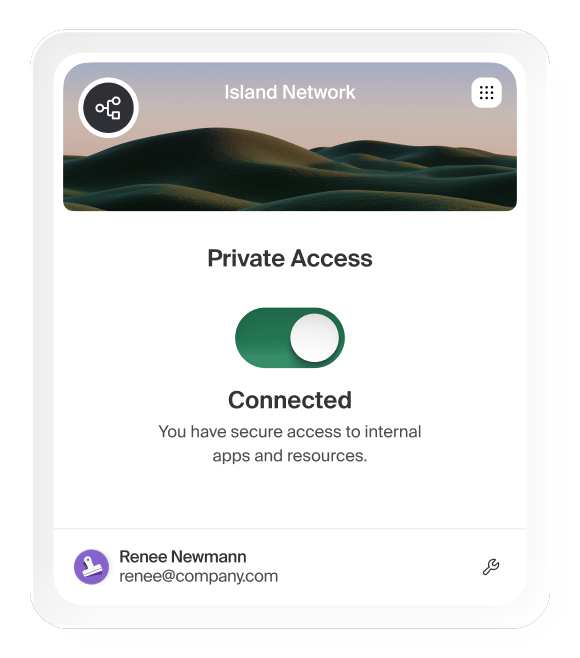
Suppliers, contractors, and agencies reach your supplier portals and engineering web apps from devices you don't manage, across plants that don't all run the same way. Control what they do in the app, not the device they're on.
Good place to start. Supplier and contractor access is a decision security, IT, and operations all have a stake in.
Plant and engineering workforce access
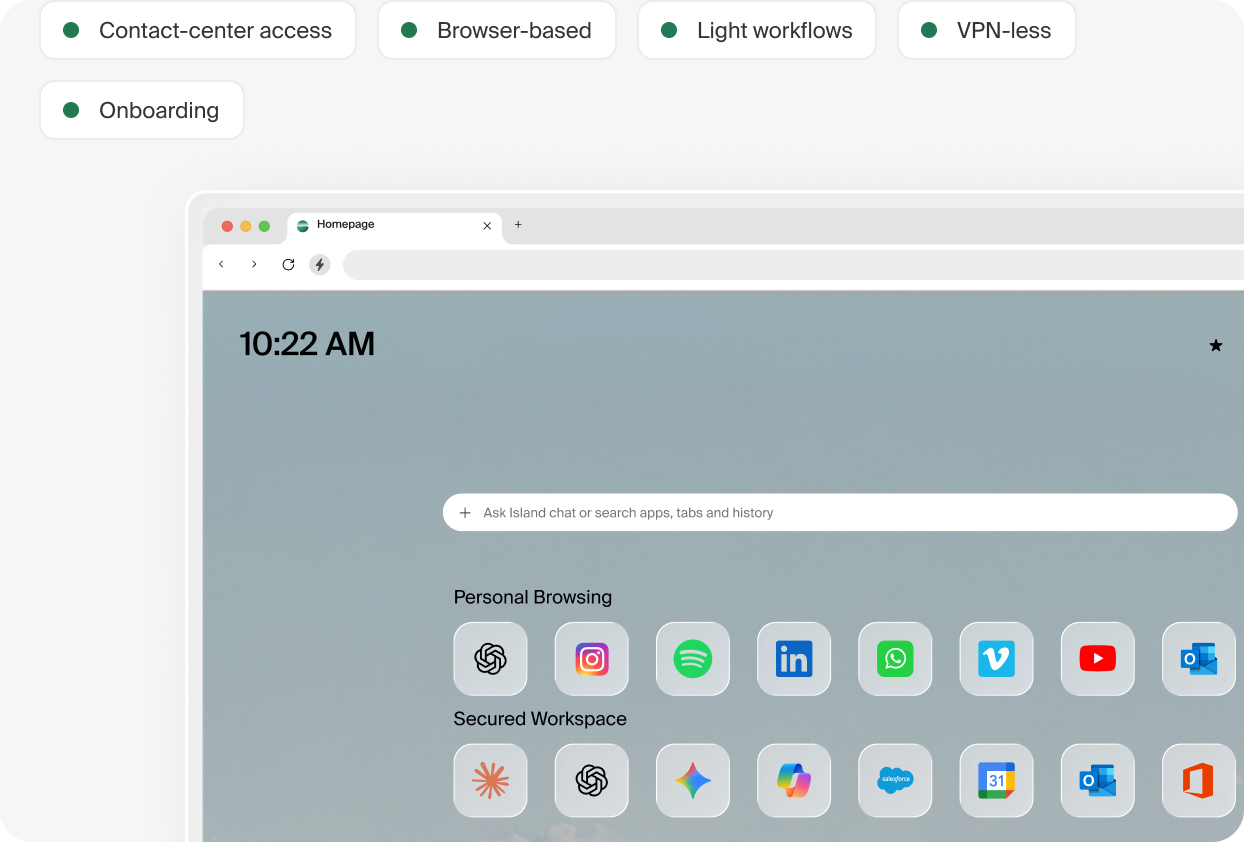
Plant staff, engineers, and partners use business and engineering web apps across every site, on managed and personal devices alike. Give them sanctioned access without shipping a laptop to every location.
A practical next step. Workforce access pulls in plant IT, security, and the people who feel the friction every day.
Engineering data and browser governance
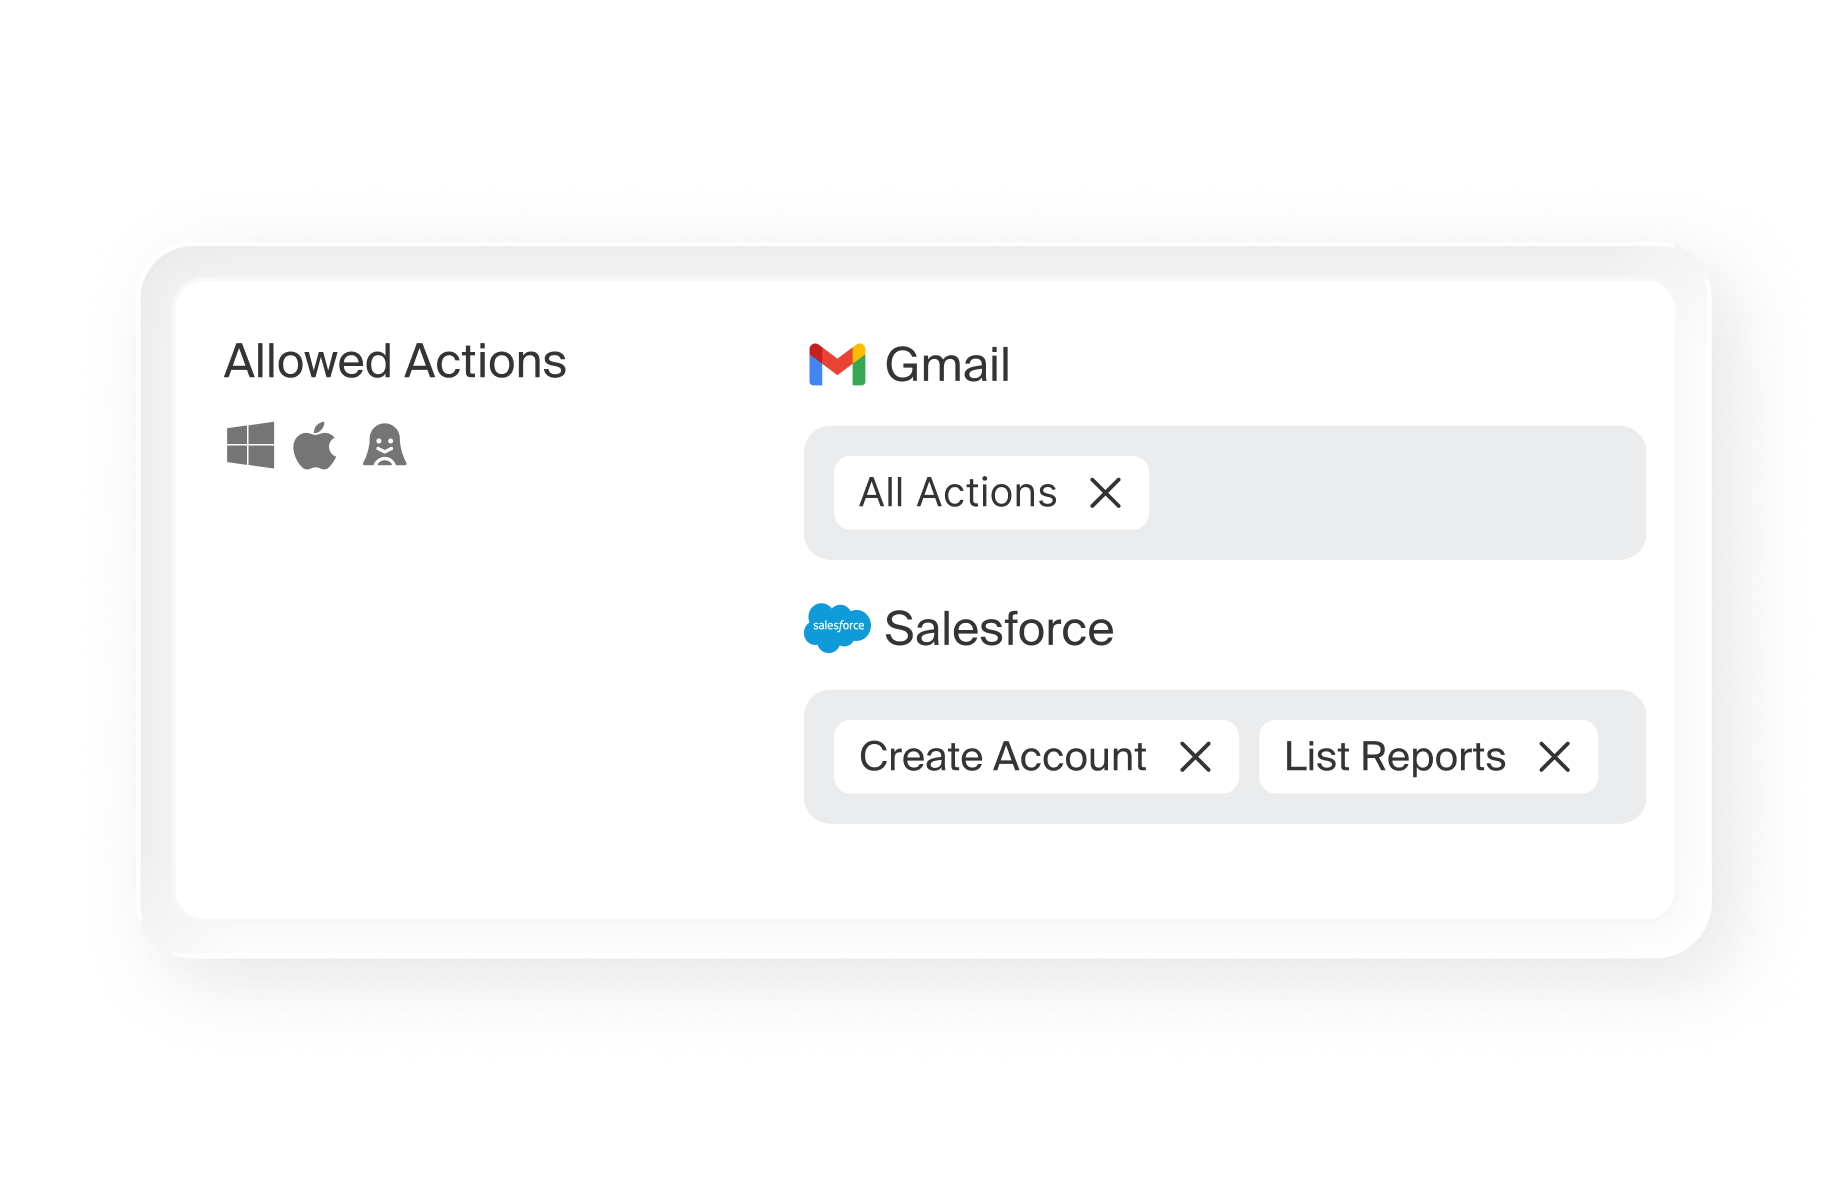
Designs, specs, and supplier data move through enterprise web apps all day, through copy, paste, download, and upload. Make the rules for that data movement explicit, and enforce them in the browser.
Increasingly the one that matters. Governing engineering and supplier data touches security, architecture, and risk alike.
Now see what tighter workflows can mean for your role
Define the data boundary after login.
Access approval is only part of it. Define what suppliers, contractors, and engineers can do with your data once they're inside supplier portals and engineering web apps.
- Session and browser policy
- Permitted data movement: copy, paste, download, upload
- Evidence for your assurance reviews
Island runs alongside your identity, endpoint, DLP, and SIEM. Nothing gets replaced.
Check the evidence behind the access model.
Assurance and procurement teams need current evidence for the requirements that apply to a supplier or engineering workflow, by region.
- Current security and privacy documentation
- Local and contractual requirements
- Evidence gaps and the assurance owner
Island deploys to a defined scope, so you can validate one workflow before anything wider.
Align supplier and workforce app access with how the business runs.
App access can span plants, suppliers, and business owners. Start with one workflow and agree on the priority before planning a broader rollout.
- The application and the accountable owner
- Access friction and deployment needs
- A practical evaluation and decision criteria
This complements what you already run and moves one workflow at a time.
Unblock one supplier workflow, with the people who own it.
Supplier portals and engineering web apps need clear ownership across IT and operations. Map one access bottleneck with the people responsible for the work.
- Supplier or contractor onboarding steps
- App access and operating ownership
- The next step, agreed with IT and security
Control at the point of work, without slowing the people doing it.
Map identity and policy to the workflow.
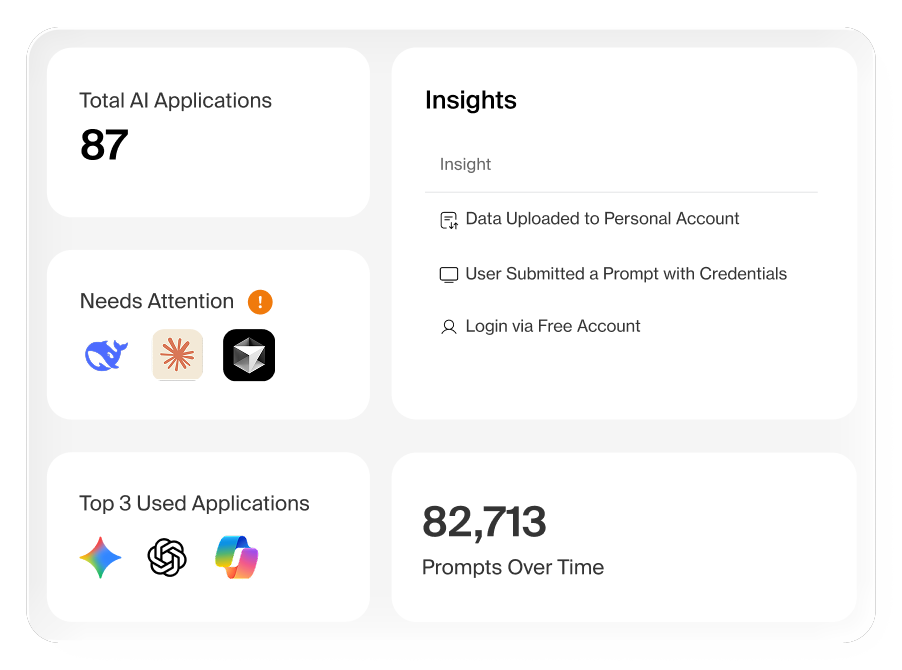
A useful evaluation starts with the application, identity, and device context. See where browser-layer policy fits in your existing access design.
- Identities, devices, and enterprise web apps
- Policy and integration requirements
- Technical discovery scoped with a solutions engineer
We use neutral criteria to show fit alongside your identity, endpoint, DLP, SIEM, and the tools you already run.
Plan deployment around workload fit.
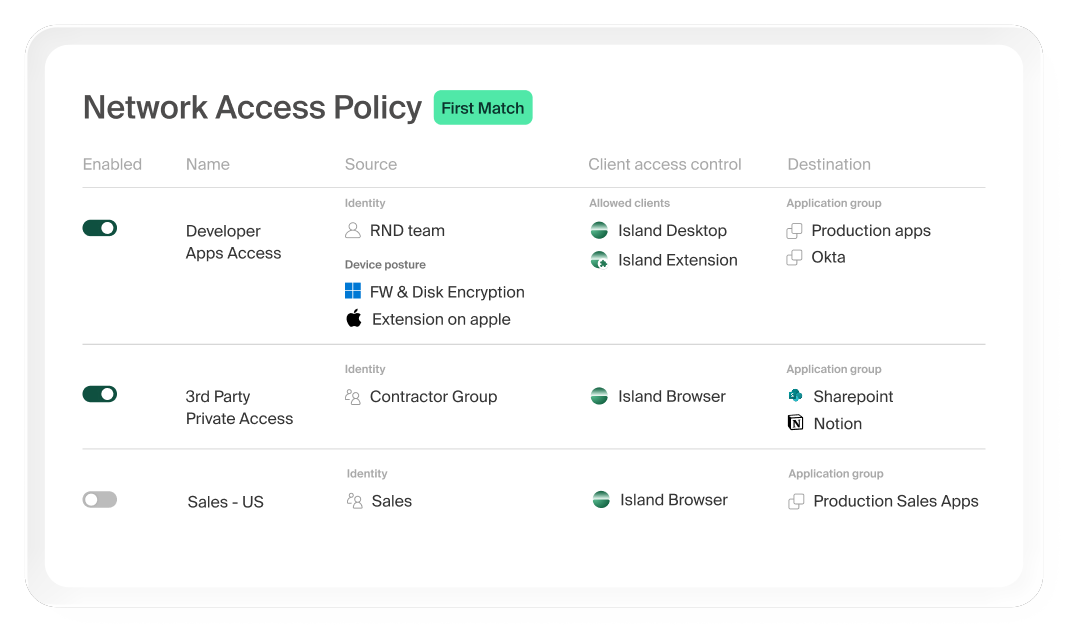
Plant IT needs a clear view of rollout, support, and the workloads in scope before changing the access approach.
- Device and support requirements
- A phased deployment and operating owner
- VDI only where browser-based workload fit is confirmed
This isn't broad VDI replacement. We score applications one at a time for browser fit and move only what makes sense.
See the results customers like you experience

Island helps us to manage risk while fueling productivity for our end users. That gives them more options for tools, rather than limiting what they can use.


Other tools are a cost center. But with Island, we’re also providing a service. That’s something people have never seen security engineering do before.


Without Island, we’d need two full-time people on staff managing this information.


Island is built for how your plants and partners actually work.
Supplier and contractor access
Fast, governed access to supplier portals and engineering web apps, without a managed device.
Plant and engineering workforce access
Secure access to business web apps across sites, with device and local privacy fit in mind.
Browser data governance
Set and enforce the rules for data movement, copy, paste, download, and upload—in the browser.
Deployment and workload fit
Map the rollout and support model. Assess VDI only for browser-suitable workloads with a verified need.
Distributed delivery
Consistent, secure access for teams in every region you operate.
SaaS and web app access
Secure the apps your people use all day, in the browser.
Data loss prevention
Control copy, paste, download, upload, and print in session.
Privileged user access
Just-in-time, least-privilege access for admin consoles and sensitive systems.
Zero trust access
Verify user, device, and context on every session.
Audit and compliance readiness
Session evidence and reporting, ready when audits come.
Want to see how Island secures manufacturing workflows?
We’ll set up a personalized walkthrough to demonstrate how we can help.
By submitting this form you consent to be contacted by Island, and acknowledge our Privacy Policy


